Find your fit
Who it is for
It suits an IT or security team that can own alert rules, review findings and respond to incidents across devices and cloud workloads. The self-managed version calls for infrastructure and operational skill; Wazuh Cloud manages the central components while endpoint enrollment and analyst decisions remain part of the customer’s workflow.
Organizations with formal audit duties may use configuration, file-change and vulnerability evidence to support review. Those controls can inform compliance work, but the buyer should map its own obligations and assess the completeness of coverage rather than treating a product report as certification.
The work it supports
Core capabilities
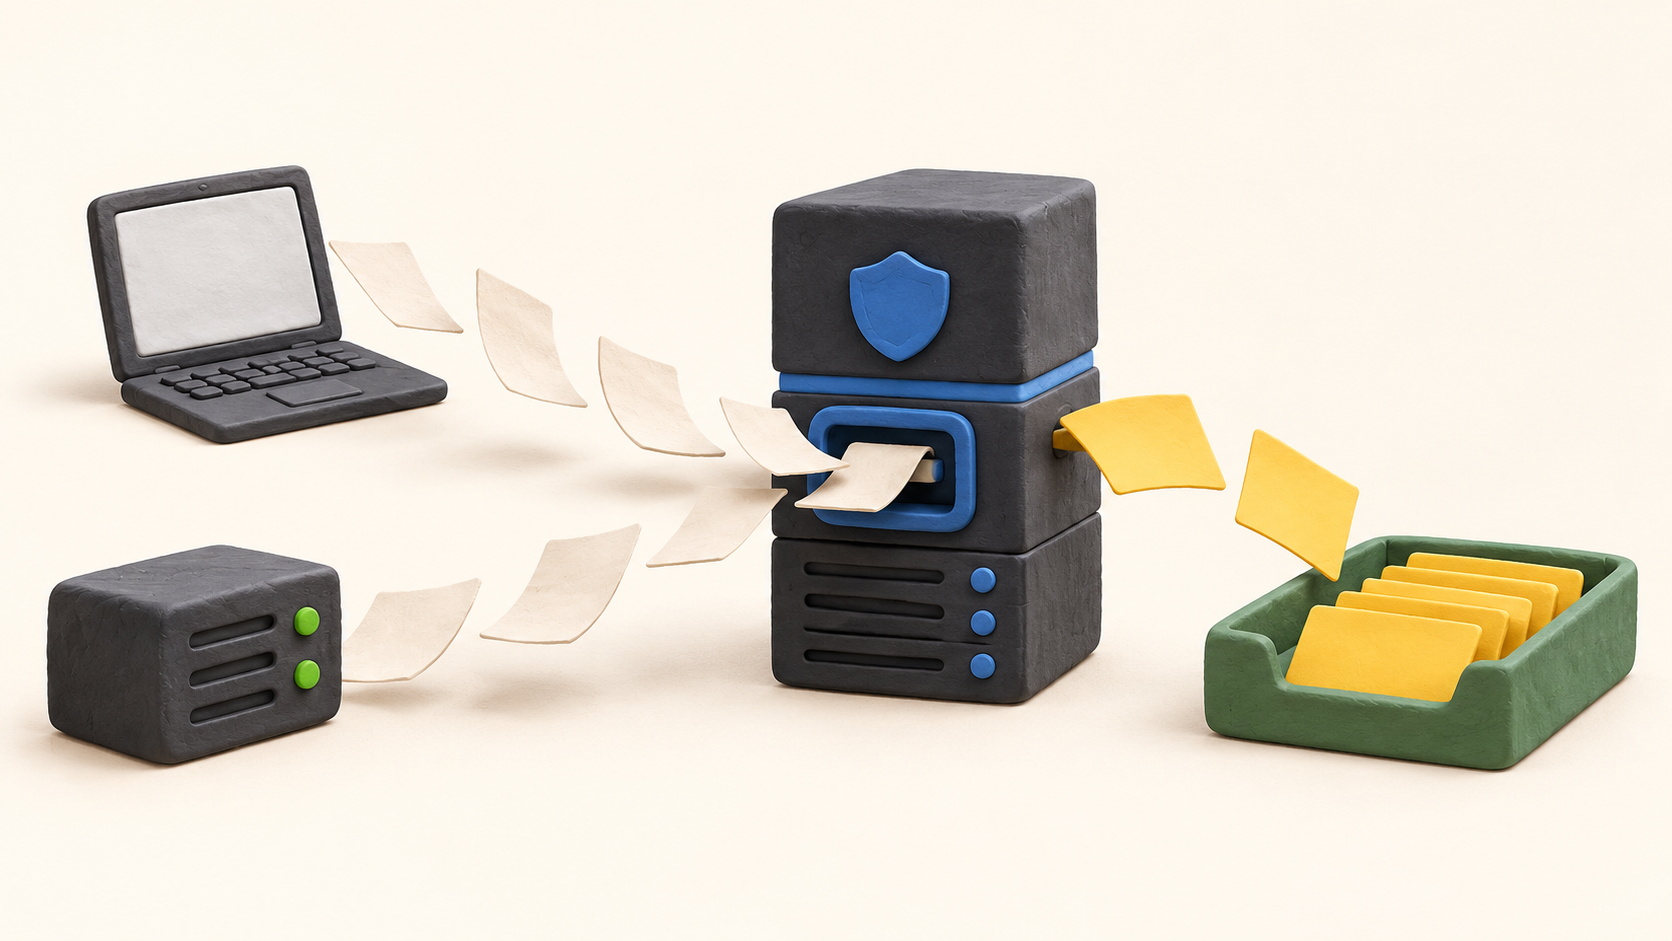
Deploy agents on the endpoints selected for monitoring. They forward operating-system and application logs to the server for rules-based analysis; the indexer makes alerts searchable and the dashboard provides a place to inspect the results.
Bring telemetry together from endpoints, network devices, cloud workloads and applications. Query retained logs and use rule mappings and threat-intelligence context to investigate an alert instead of acting on one signal alone.
Run configuration assessments against system and application settings to surface misconfigurations. File integrity monitoring can track selected changes to content, permissions, ownership and attributes; define important files and expected change windows before enabling noisy checks broadly.
Correlate installed-software inventory with CVE data to surface known vulnerabilities. This helps prioritize investigation, but operators still need to verify an affected version, exposure and remediation path.
Configure active responses for carefully chosen conditions, such as blocking access from a threat source. Test the rule and rollback path in a safe environment before allowing automation to affect production connectivity.
Use alerts, dashboards and reports to review events and communicate findings. A useful trial should examine alert volume, investigation context and the work needed to tune rules for the organization’s systems.
In Wazuh Cloud, the vendor hosts and updates central components and advertises weekly AI-generated analyst reports and CTI access. Those are Cloud-specific services; verify their fit and terms separately from a self-managed installation.
Understand the offer
Pricing and getting started
The main Wazuh platform is open source and can be installed in an organization-managed environment. Wazuh Cloud is a separate managed service for the central components. Compare infrastructure, operations and support ownership before treating the open-source license as the entire cost.
The public Cloud page displays starting amounts of $571 per month for Small (up to 100 active agents), $923 for Medium (up to 250), and $1,467 for Large (up to 500). Those are starting displays, not a fixed quote for every data volume or configuration; confirm current currency and contract terms.
The same Cloud profiles differ in indexed and archived data retention: Small shows one and three months, while Medium and Large show three months and one year. A Custom environment is available for other needs. Estimate agent count, event volume and retention before selecting a tier.
Wazuh advertises a 14-day Cloud trial. Its setup guide notes that some environment choices are restricted during the trial, so test a representative agent and review the actual plan options before extrapolating to production.
Look a little closer
Before you choose
Start with a limited set of endpoints and one log source. Confirm agents are reporting, create a harmless known test event, follow it through server analysis into the dashboard, and note whether an analyst can explain the alert and suppress expected noise.
Agree on who triages vulnerability findings, configuration drift and changed files. These signals need context and follow-through; tune the monitoring scope and alert rules before broad deployment.
Evaluate any active response with an isolated test and a recovery procedure. A misfired network block can disrupt legitimate traffic, so production automation needs an owner and a way to reverse it.
For Cloud, calculate agents and required indexed/archive retention, then compare the visible starting price with a current quote. For self-management, identify who maintains the server, indexer, dashboard and backups. Keep the separate Wazuh Lumen and Argus offerings outside this platform evaluation.
5 distinct sources behind this profile. Research observed Oct 18, 2026. Features and offers can change.
View sources and research →
