Find your fit
Who it is for
A small team replacing broad VPN access can start with one internal application, assign it to a limited Group and verify that other Resources remain unavailable. Twingate is particularly relevant when access should follow identity and the specific application, rather than a network-wide connection. Its usefulness depends on clean Resource boundaries and a Connector that can actually route to each destination.
IT teams with multiple sites or cloud networks can group Resources into Remote Networks and deploy Connectors close to those destinations. Identity-provider synchronization and policy controls may reduce manual access upkeep, but the tier and configured identity provider determine which automation is available. Confirm routing, group mapping and device requirements with a small fictional setup before rollout.
The work it supports
Core capabilities
A Resource can represent a private DNS name, private IP address or CIDR range as long as a Connector in its Remote Network can resolve and route to it. Wildcard names and broad ranges are possible; define the narrowest useful address and test it before granting a Group, because the address boundary determines what that grant covers.
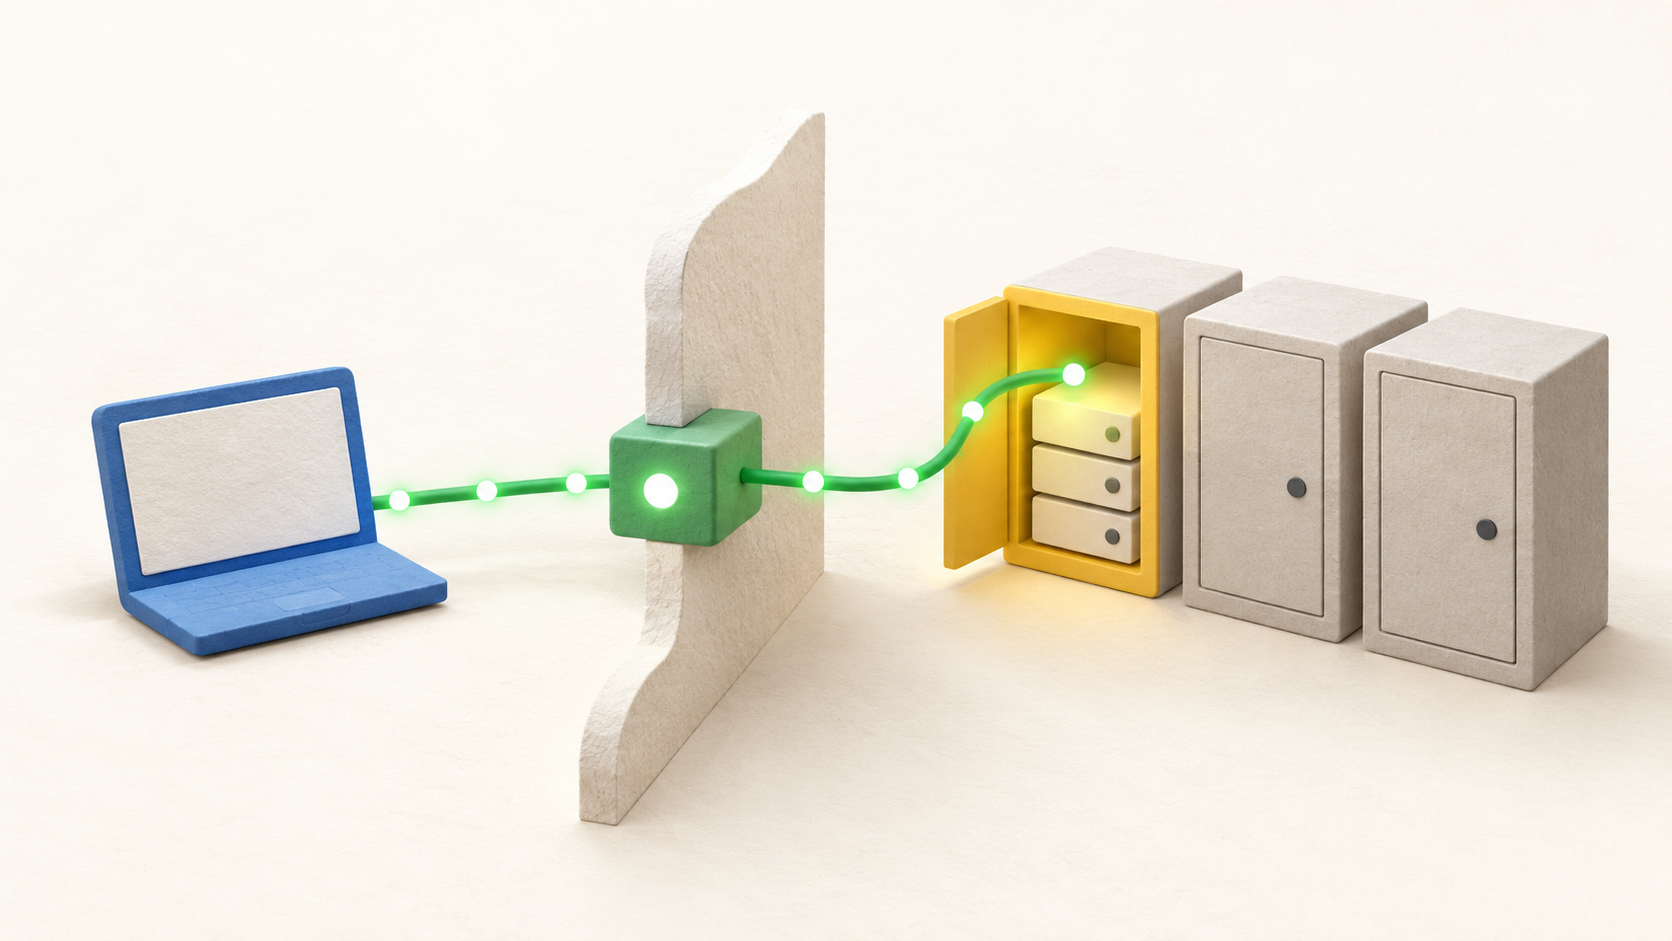
Connectors run behind the firewall as containers or Linux services. Twingate documents scripts for Docker, Kubernetes, Azure, Linux and AWS deployments. A Remote Network groups Resources reachable from its Connectors; at least one is required, and the vendor recommends two for redundancy. A pilot should verify routing and recovery if a Connector goes offline.
The Client runs on macOS, Windows, Linux, iOS, Android and ChromeOS. It intercepts private-Resource traffic locally, while users continue to open an authorized browser, SSH or RDP destination in the usual way. Check the operating system and installation route for every device type in scope, including managed endpoints.
A user can be added manually or synchronized from an identity provider. Group membership governs Resource entitlements; a new user starts with only the Everyone group and no Resource access unless a Resource is granted through it or another Group. The Access Graph provides a useful review of which Group and policy path gives a user access.
Every new Resource receives a Default Policy, which an administrator can edit or replace. Resource Policies can ask for reauthentication and MFA and can set device rules. A Group may receive a policy override for the same Resource, so inspect both the Resource policy and group assignments when troubleshooting an unexpected prompt or access result.
Authorization to a Resource can expire under its Security Policy, requiring the user to authenticate again. Twingate documents an extra prompt for Resources with stricter requirements than the network minimum. Test a normal session and an expired one with a fictional Resource so support staff know what the user will see.
Enterprise adds geographic location requirements. This is a plan-specific control rather than a default rule for every account. If location is part of an access policy, confirm the contracted tier and test the actual permitted and blocked cases before relying on it.
Understand the offer
Pricing and getting started
The public Starter card is free for up to five users, with a comparison-grid limit of 50 Resources. Home is listed at $15 per month for up to seven users, but its terms restrict it to non-commercial use. A business should compare the commercial Teams, Business or Enterprise tiers rather than treating Home's feature list as a low-cost business package.
The currently displayed Teams card shows $5 per user per month for up to 100 users and lists Google Workspace SSO and native posture checks. Business shows $10 per user per month for up to 500 users and lists broader IdP provisioning, Okta/Entra SSO and service accounts. The page also advertises a yearly discount, so confirm selected billing term, currency, exact entitlements and total in a dated quote.
Enterprise is quote-led, with custom account sizes, invoicing and geoblocking. The pricing page marks DNS filtering, static IPs and certain support options as add-ons. List each required policy, service-account and support feature in the quote; a capability on the comparison page may sit outside the chosen tier or base price.
Twingate's licensing page counts Users and Service Accounts, including pending and disabled users, admins, manual users and IdP-synced users. Monthly and annual renewals use those totals, and annual additions may be prorated. Model the expected synced population and offboarding process before estimating spend; the vendor says Enterprise arrangements can differ.
Home, Teams and Business cards advertise a 14-day trial. A downgrade is scheduled for the next billing date. Before a trial or purchase, check which tier is active, when it renews, how many users and service accounts count, and whether any add-on remains enabled after a change.
Look a little closer
Before you choose
For a safe evaluation, use invented Resource names and a nonproduction destination: define one narrow address, confirm the Connector can resolve it, grant one test Group and leave a second Group without access. Review the Access Graph and both allowed and denied outcomes. This tests the access boundary without touching a customer system.
Map every Remote Network to the actual site or VPC it represents, then check Connector reachability and redundancy. A broad wildcard or CIDR grant can have a larger scope than a single host; a Group-level policy override can persist after a Resource policy changes. Include both in change review and document who may modify them.
During procurement, compare the identity provider and device controls you need against the selected plan, then count synced, pending, disabled and service-account licenses. Include Home's non-commercial restriction and Enterprise-only geoblocking where relevant. Ask for a written renewal and add-on schedule rather than relying on a single public per-user amount.
11 distinct sources behind this profile. Research observed Oct 26, 2026. Features and offers can change.
View sources and research →
