Find your fit
Who it is for
It fits teams replacing scattered shared passwords with named access to a common set of credentials. Administrators can plan folder and group membership so people receive only the secrets needed for their work, then remove access when roles change.
Self-hosting suits an organization prepared to run and maintain the server and its access paths. The SaaS route shifts updates, backups and maintenance to the vendor. Decide which operational model is acceptable before comparing editions or paid terms.
The work it supports
Core capabilities
Psono's client and server design encrypts passwords, notes and bookmarks in the browser before storage. Teams should still define their own recovery and access procedures, especially for the self-hosted server and any identity integration.
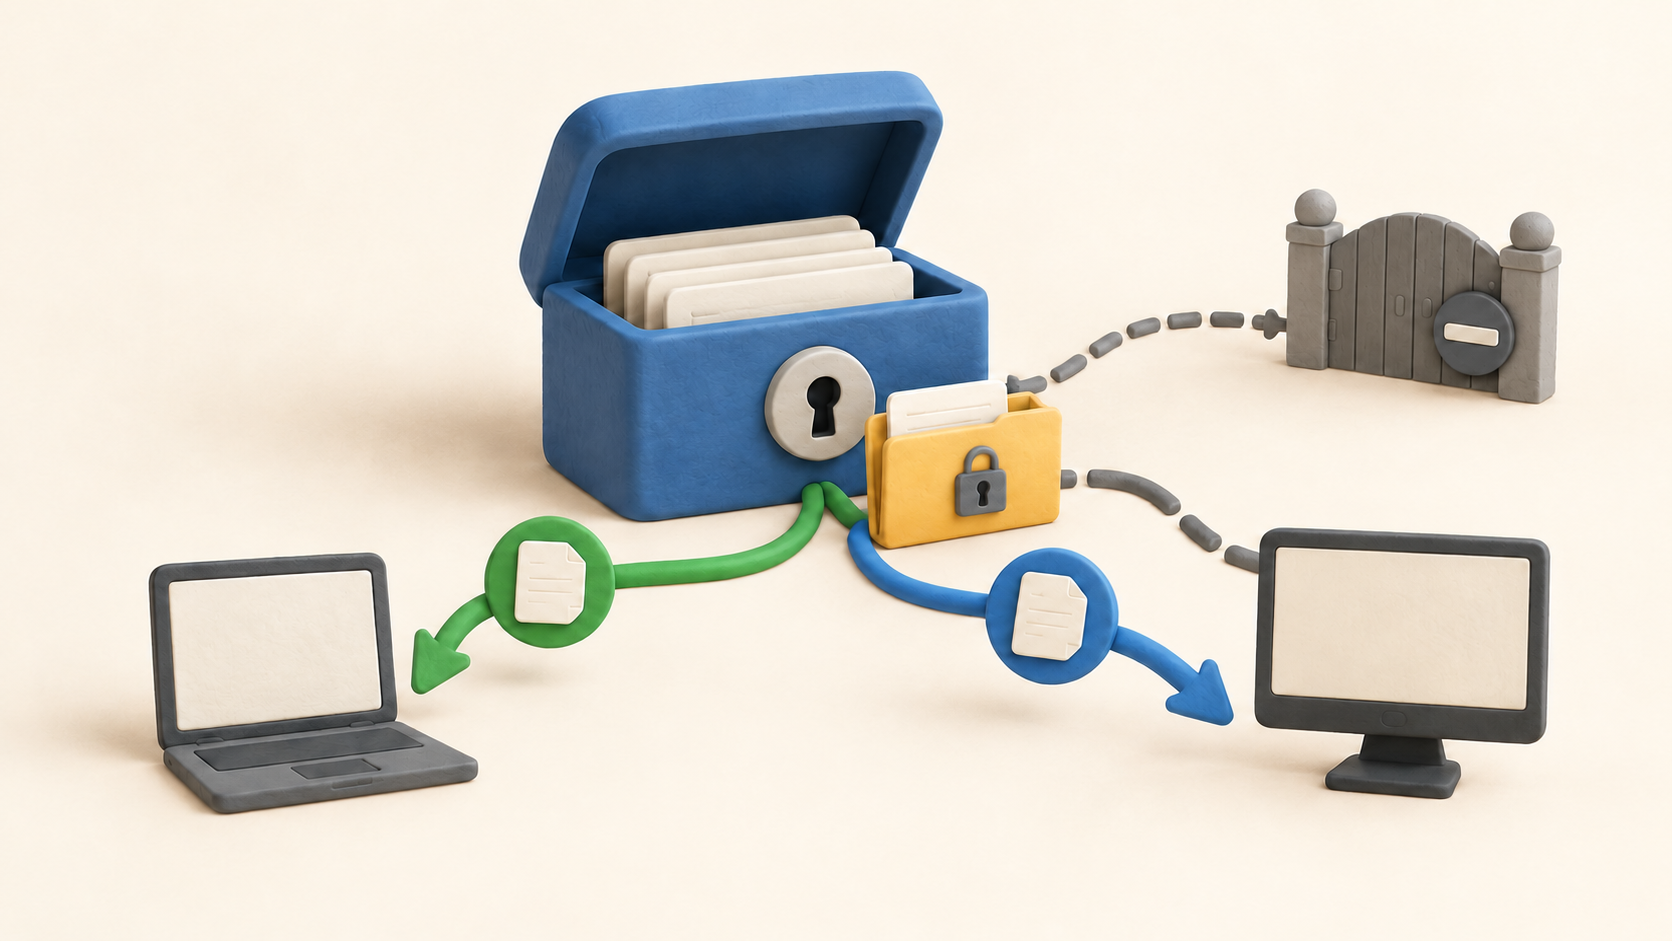
A user can share a secret or an entire folder with another user or group. Read permits viewing, write permits editing, and grant permits changing access rights or sharing onward. Start with a small group-based folder and verify each role before moving high-value credentials.
Psono also describes link sharing with people who do not have an account. Because that changes who can receive a secret, check recipient identity, network reachability and the organization's link-sharing policy before using it.
Browser autofill, password generation and security reports support everyday use. The reports address age, complexity and length; an organization should test how imported entries, multiple accounts and autofill behave on its actual websites.
The product lists multifactor methods including YubiKey, Duo, TOTP apps and WebAuthn/passkeys, plus browser, desktop and mobile clients. Test enrollment, lost-device recovery and access from the organization's managed devices before rollout.
Enterprise Edition adds LDAP/SAML/OIDC integration, audit logging and policies such as requiring MFA or disabling exports. The admin documentation says SAML/OIDC needs a server-side path to users' secrets for login. Review that key-handling model and the selected edition with a security owner before assuming the same trust boundary as a basic login.
Understand the offer
Pricing and getting started
Psono advertises open-source and business editions. Its FAQ says password management is free for teams up to ten users; confirm the included features and whether the allowance applies to the intended SaaS or self-hosted deployment.
For larger teams, the FAQ describes a per-user paid model with a minimum of 25 users, while saying total cost depends on the organization's size. Ask Psono for a written quote covering deployment, seats, Enterprise features and support before budgeting; this profile does not rely on one public starting amount.
Self-hosting means the organization operates its own server. Psono says its SaaS route handles updates, backups and maintenance, while professional support or SLA terms are quote-led. Include internal hosting effort and any service requirement in the comparison.
Look a little closer
Before you choose
Pilot a representative credential set: import a few entries, create a group folder, grant read or write rights, then revoke one member and confirm the result. Test export and recovery procedures without placing production secrets in the pilot.
If SSO is required, examine Psono's documented server-side secret-access requirement alongside the organization's key-handling policy. Test the actual identity provider and recovery flow before making SSO the only way into a critical vault.
Verify the exact edition, deployment model, free-user allowance, paid seat minimum and support terms with the vendor. Use a written quote that names each item as the basis for budget approval.
7 distinct sources behind this profile. Research observed Oct 20, 2026. Features and offers can change.
View sources and research →
