Find your fit
Who it is for
It is aimed at software teams handling API keys, credentials, tokens and other sensitive application configuration across local development, CI/CD and production. A team replacing scattered environment files or copied values can evaluate one project and one deployment pipeline before widening access.
It can also fit a team that needs workloads to retrieve values under a machine identity, or that must keep another platform populated through secret syncs. The useful question is where each secret should be the source of truth and how the consuming service will authenticate.
The work it supports
Core capabilities
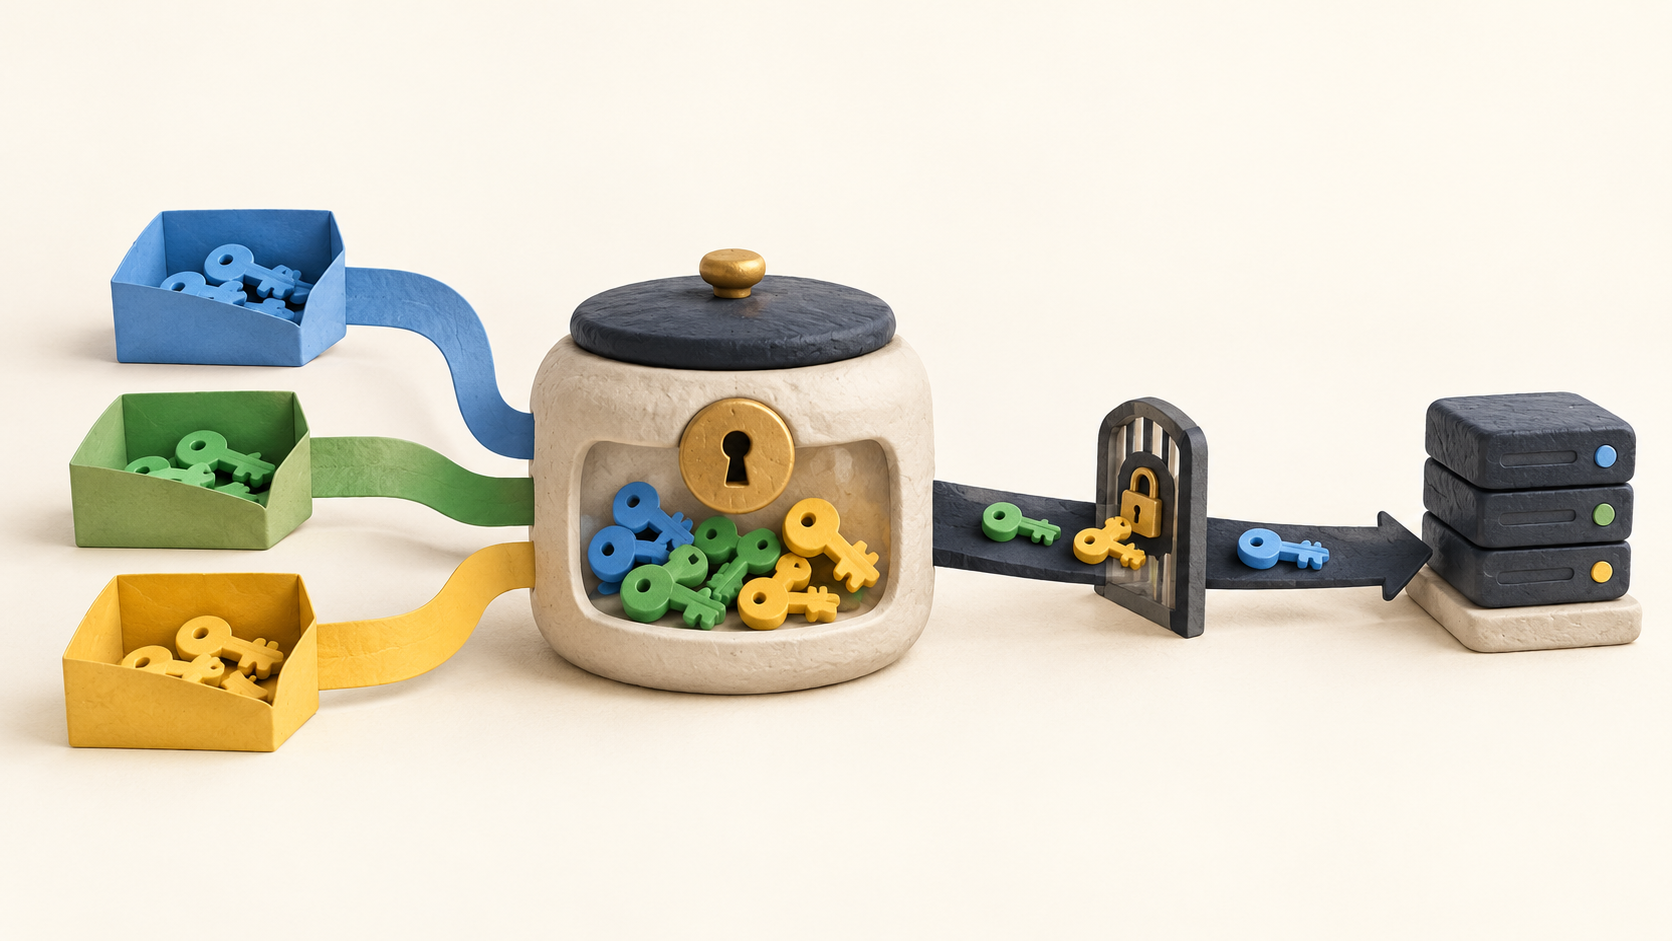
Start with a secrets-management project inside an organization. Divide values into environments such as development, staging and production, then use folders where a service or region needs a smaller scope. This structure helps a team keep similarly named configuration values separate.
Store ordinary name-value secrets alongside multiline or structured values. References and imports can reuse a shared value in several places, avoiding manual copies when an underlying credential changes.
Deliver values where code runs. The vendor describes CLI injection for a developer’s local process, agents beside workloads, and several Kubernetes delivery options. Choose the least disruptive method for the application and test how it behaves when a value changes.
Where a destination expects its own secret store, a secret sync can push a value outward while Infisical remains the managed source. Confirm the specific destination, update timing and sync quota before depending on it in production.
Assign access to human or machine identities at project, environment and path scope. Some integrations can authenticate through the workload’s existing identity, avoiding a static credential embedded in that workload. Test a restricted identity against the exact path it should read.
Change history and recovery tools can help inspect an individual secret version or restore a group to an earlier point. Audit logs provide a record of access and changes. The current pricing page gates versioning, recovery and stated retention by plan, so confirm the needed history before selecting a tier.
Scheduled secret rotation and on-demand dynamic secrets are available in the product family. Rotation is listed in Pro, while dynamic secrets are listed in Advanced; verify that the chosen integration supports the desired credential and expiry behavior.
Understand the offer
Pricing and getting started
The current Free tier lists five identities and unlimited projects, plus limits including three environments and ten secret syncs. An identity can be a person or a machine, so a growing CI/CD estate can use the allowance quickly.
Pro and Advanced are presented as paid per-identity plans with annual billing and 14-day trials; Enterprise uses a sales conversation. The comparison places access controls, rotation, versioning and recovery in Pro; dynamic secrets, custom roles and temporary access in Advanced; and approval workflows, SCIM and self-hosting or dedicated infrastructure in Enterprise. Check the current quote and feature table for the intended deployment.
Infisical describes EU and US cloud regions and the ability to self-host. Because the pricing comparison names self-hosting or dedicated infrastructure under Enterprise, confirm licensing, support and operating responsibilities before choosing a self-hosted route.
Look a little closer
Before you choose
Map existing secrets by project, environment, owner and consuming service before importing them. Decide which shared values should use references and which should remain separate; then pilot a small set to check that each workload sees only its intended environment.
Test one delivery route end to end with a restricted machine identity. Include an ordinary update and a failed authentication case, especially where a sync or Kubernetes integration adds another system between Infisical and the application.
Count both people and machines when comparing plans, and check environment, sync, audit-history and recovery requirements. Treat rotation and dynamic secrets as separate plan and integration decisions rather than assuming they are included in Free.
3 distinct sources behind this profile. Research observed Oct 19, 2026. Features and offers can change.
View sources and research →
