Find your fit
Who it is for
Infrastructure or security operators who can configure log sources and an enforcement point can use it to observe suspicious behavior and choose where to act. The setup calls for testing both detection and the separate blocking path against their actual services.
A team with several installations may use the separate Console to see enrolled engines and manage added blocklists. Decide whether the free engine and account meet the need before budgeting for Console Premium or commercial threat-data use.
The work it supports
Core capabilities
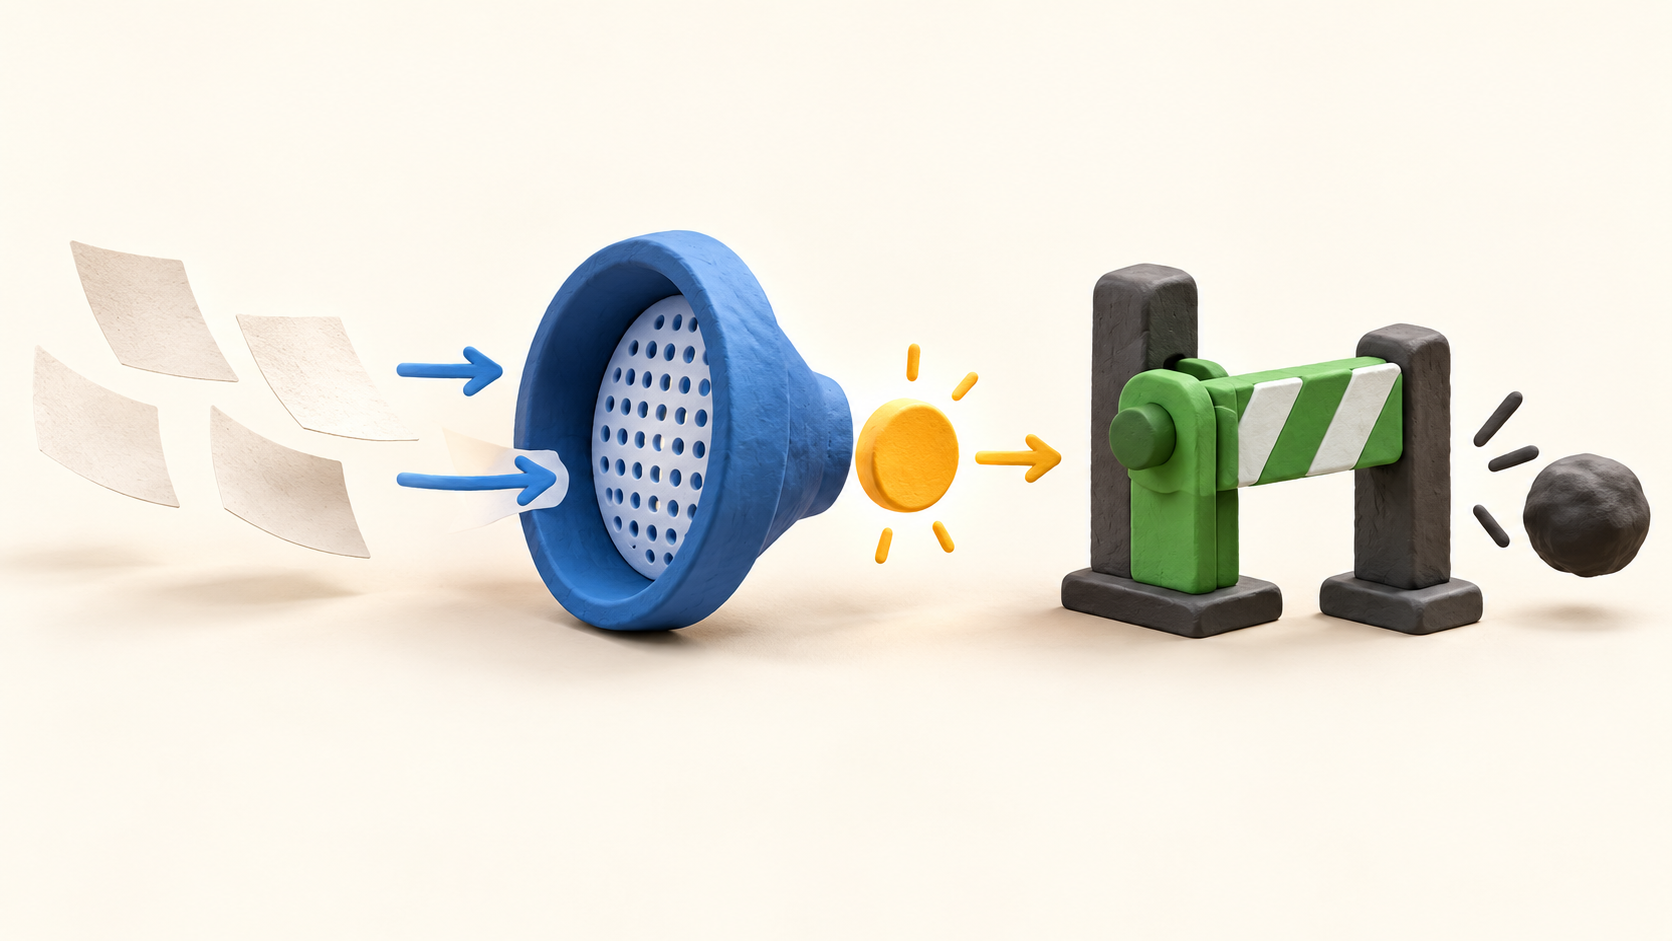
The Log Processor reads the data sources defined in acquisition files. Parsers normalize events, enrichers add context, and scenarios look for behavior patterns before alerts go to the Local API. Confirm that the intended service logs are actually being collected.
Collections bundle parsers, scenarios and enrichers for an application; the documentation gives NGINX as an example. Scenarios can produce alerts from repeated or other defined behavior, while profiles can turn qualifying alerts into decisions. Tune the selected collections and inspect false positives on representative traffic.
Remediation Components enforce engine decisions through the Local API. CrowdSec documents both firewall enforcement and an embedded NGINX path. Choose the point that matches your traffic path; the engine detects but does not block by itself.
The Console gives a centralized view of enrolled engines and extra blocklist management. This web service is distinct from the local Security Engine. Check which engines appear and how their status and alerts map to the systems you protect.
CrowdSec offers a community blocklist whose tier depends on contribution or a paid subscription. Only signals from unmodified official Hub scenarios count toward free community contribution. A custom scenario may still trigger local alerts without making the deployment eligible for the fuller shared list.
The vendor says engine log analysis stays local, but community signal sharing is opt-in. Review the actual data-sharing, account and Console settings against your privacy and retention requirements before connecting a production system.
Understand the offer
Pricing and getting started
CrowdSec describes the Security Engine as free and open source and advertises a free Console account. Running and maintaining the engine, its log sources and any enforcement component remain operational work for your team.
Console Premium adds management and blocklist features, with pricing described as pay as you grow per enrolled Security Engine. The captured public page does not establish a clear standalone monthly rate, so request current terms for the intended engine count.
Current docs put three additional blocklist subscriptions on the Community Console plan and say Premium removes that limit. Commercial embedding or resale of CrowdSec security data has a separate partnership model and pricing.
Look a little closer
Before you choose
Verify the protection path end to end. The troubleshooting guide warns that an engine with no registered Remediation Component will detect but not enforce decisions. A detection-only node or external perimeter integration can be intentional; document that route and test its actual action on safe traffic.
Check log acquisition and scenario coverage for each protected service, then review decision behavior before enforcing. A scenario alert is a detection event, while the remediation layer is the distinct action point.
Check the current Console plan and community contribution status rather than assuming all blocklists are included with the free engine. Modified or custom scenarios do not count as community signals under the captured eligibility rules.
10 distinct sources behind this profile. Research observed Oct 18, 2026. Features and offers can change.
View sources and research →
